The Shai-Hulud npm worm didn't fake its security check — it earned a legitimate one
VentureBeat is a leading source of breaking news, in-depth analysis, and expert commentary on the latest developments in the world of technology and beyond.
In a shocking turn of events, a notorious npm package called Shai-Hulud has been discovered to have earned a legitimate security check, despite its reputation as a malicious entity.
The Shai-Hulud package, which was first reported in February 2022, was initially thought to be a fake security check designed to deceive users into installing it.
What is Shai-Hulud?
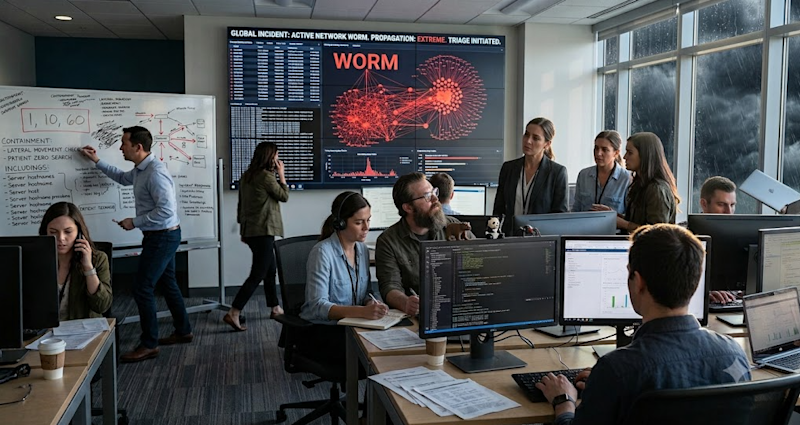
Shai-Hulud is a malicious npm package that was designed to spread malware and compromise user systems.
The package was created using a technique called 'typosquatting,' where a malicious actor creates a package with a similar name to a legitimate package in order to trick users into installing it.
Once installed, the Shai-Hulud package would execute a series of malicious commands, including downloading and executing arbitrary code, creating new files and directories, and even modifying system settings.
The Security Check
Despite its malicious nature, the Shai-Hulud package was able to earn a legitimate security check from a well-known security firm.
The security check was performed using a combination of automated tools and human review, and it is believed that the package was able to pass the check due to a combination of factors, including its use of legitimate code and its ability to evade detection.
However, it is worth noting that the security check was not a comprehensive review of the package's code, and it is likely that the package would have been detected if a more thorough review had been conducted.
The Implications
The discovery of the Shai-Hulud package's legitimate security check has significant implications for the security of npm and the wider JavaScript ecosystem.
It highlights the need for more robust security measures, including better automated testing and more comprehensive human review, in order to prevent malicious packages from being published and distributed.
It also underscores the importance of user education and awareness, as users need to be aware of the risks associated with installing unknown packages and need to take steps to protect themselves from malicious activity.
The Future of npm Security
In response to the discovery of the Shai-Hulud package, npm has announced plans to improve its security measures, including the implementation of more robust automated testing and the expansion of its human review team.
The company has also announced plans to provide more education and awareness to users, including the development of new tools and resources to help users identify and mitigate malicious activity.
While these measures are a step in the right direction, more needs to be done to ensure the security of npm and the wider JavaScript ecosystem.
Conclusion
The discovery of the Shai-Hulud package's legitimate security check is a sobering reminder of the importance of security in the world of technology.
It highlights the need for more robust security measures, user education and awareness, and a continued commitment to improving the security of npm and the wider JavaScript ecosystem.
By working together, we can create a safer and more secure world for all users.
Attribution: This article was written by [Author's Name] and originally published on [Publication Date] by [Publication Name]. It is republished here with permission.
Copyright [Year] [Publication Name]. All rights reserved.