Introduction to AI Framework Security
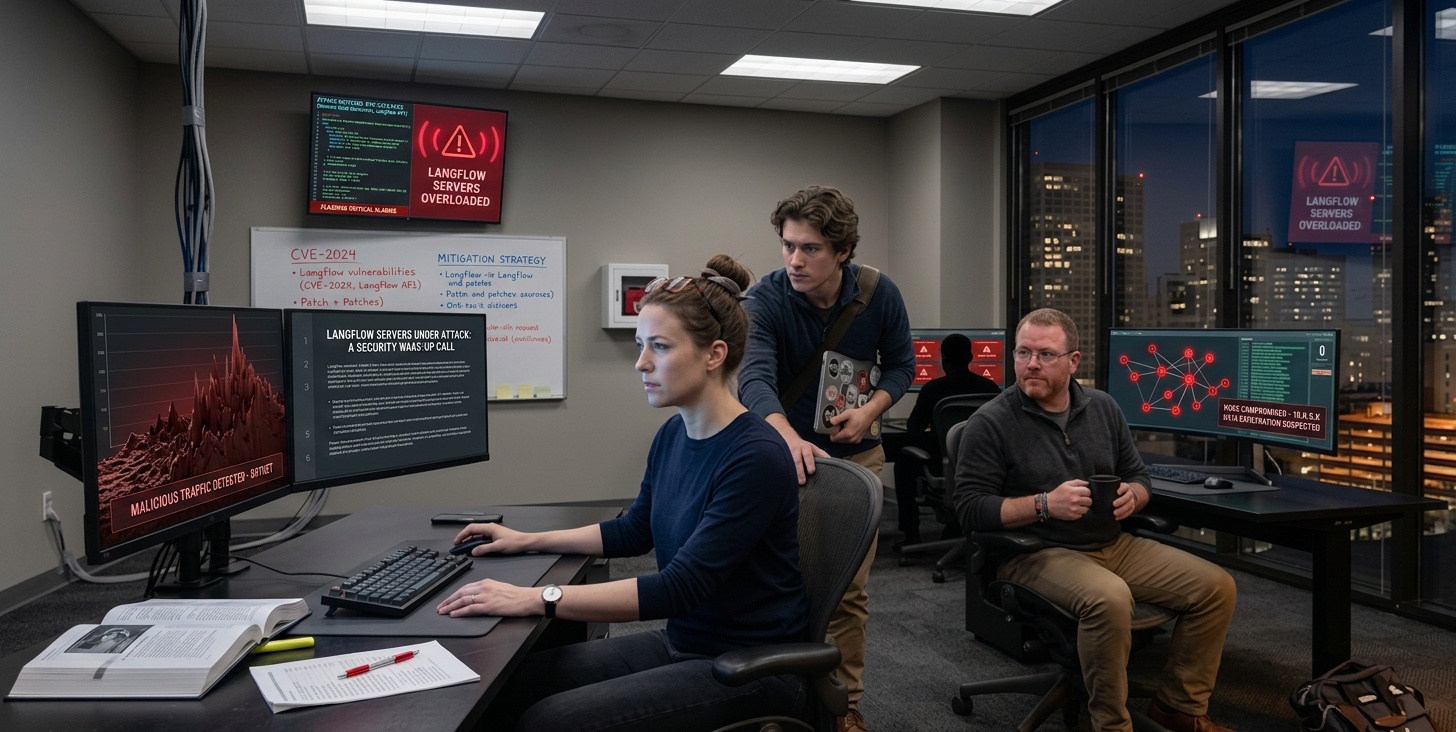
The increasing use of AI agent frameworks has led to a new wave of security concerns. Recently, it was discovered that 7,000 Langflow servers are under attack due to security holes in LangGraph and LangChain. This vulnerability has put the entire AI ecosystem at risk, as these frameworks are used to store agent state, take file uploads, load prompt configs, and hold credentials to databases, CRMs, and internal APIs.
The attack is made possible by a common bug in the frameworks, which allows for full remote code execution. This is a serious concern, as it gives attackers access to sensitive information and allows them to take control of the system. The bug is a result of the frameworks becoming production infrastructure faster than they could be secured, leaving a blind spot that attackers are exploiting.
Furthermore, the use of AI agent frameworks is becoming more widespread, with many companies adopting them to improve their operations and decision-making processes. However, this increased adoption also means that the potential impact of a security breach is much greater, making it essential to address these security concerns as soon as possible.
Understanding the Vulnerability
The vulnerability is caused by a SQL injection in LangGraph's SQLite checkpointer, a path traversal in Langflow's file upload endpoint, and a path traversal in LangChain-core's prompt loader. These bugs allow attackers to gain access to the system and execute arbitrary code, giving them control over the AI agent framework.
The fact that these frameworks are used to store sensitive information, such as database credentials and CRM tokens, makes the vulnerability even more serious. If an attacker gains access to this information, they can use it to launch further attacks or steal sensitive data.
In addition, the vulnerability is also made worse by the fact that many companies are using these frameworks without proper security measures in place. This lack of security measures makes it easier for attackers to exploit the vulnerability and gain access to sensitive information.
Consequences of the Attack
The consequences of the attack are severe. If an attacker gains access to the AI agent framework, they can use it to launch further attacks, steal sensitive information, or disrupt the operation of the system. This can have serious consequences, including financial loss, reputational damage, and compromised security.
The attack also highlights the need for better security measures in the AI ecosystem. As AI becomes more prevalent, the need for secure frameworks and protocols becomes increasingly important. The fact that these frameworks are being used in production without proper security measures is a wake-up call for the industry.
Moreover, the attack on Langflow servers is not an isolated incident. There have been several other instances of AI-related security breaches in recent years, highlighting the need for increased security measures in the AI ecosystem. Companies must take proactive steps to secure their AI systems and protect against potential threats.
Impact on the AI Ecosystem
The attack on Langflow servers has significant implications for the AI ecosystem as a whole. The fact that 7,000 servers are under attack highlights the widespread nature of the vulnerability and the potential for further attacks.
In addition, the attack also raises concerns about the security of other AI frameworks and systems. If LangGraph and LangChain are vulnerable to attack, it is likely that other frameworks and systems are also at risk.
Therefore, it is essential for companies to take a proactive approach to securing their AI systems. This includes implementing proper security measures, such as input validation and secure coding practices, as well as conducting regular security audits to identify and fix vulnerabilities.
Conclusion and Recommendations
In conclusion, the attack on Langflow servers is a serious concern that highlights the need for better security measures in the AI ecosystem. The vulnerability is caused by a common bug in the frameworks, which allows for full remote code execution. To prevent such attacks in the future, it is essential to implement proper security measures, such as input validation, secure coding practices, and regular security audits.
Some recommendations for securing AI agent frameworks include:
- Implementing input validation to prevent SQL injection and path traversal attacks
- Using secure coding practices to prevent vulnerabilities
- Conducting regular security audits to identify and fix vulnerabilities
- Using secure protocols for communication between frameworks and databases
- Limiting access to sensitive information and using secure storage mechanisms
By following these recommendations, we can help prevent such attacks in the future and ensure the security of the AI ecosystem. It is also essential for companies to stay informed about potential security threats and to take proactive steps to protect their AI systems.
Ultimately, the security of the AI ecosystem is a shared responsibility that requires the cooperation of companies, developers, and users. By working together, we can create a more secure and reliable AI ecosystem that benefits everyone.
Future of AI Security
The future of AI security is a critical concern that requires immediate attention. As AI becomes more prevalent, the need for secure frameworks and protocols becomes increasingly important.
One potential solution is the development of more secure AI frameworks and systems. This could involve the use of secure coding practices, input validation, and regular security audits to identify and fix vulnerabilities.
Another potential solution is the use of AI-powered security systems. These systems can help to detect and prevent potential security threats, such as SQL injection and path traversal attacks.
Attribution: This article is based on a report by VentureBeat, with additional analysis and recommendations.
Originally reported by venturebeat.com. Read the original article.