Introduction to Autonomous Security Agents
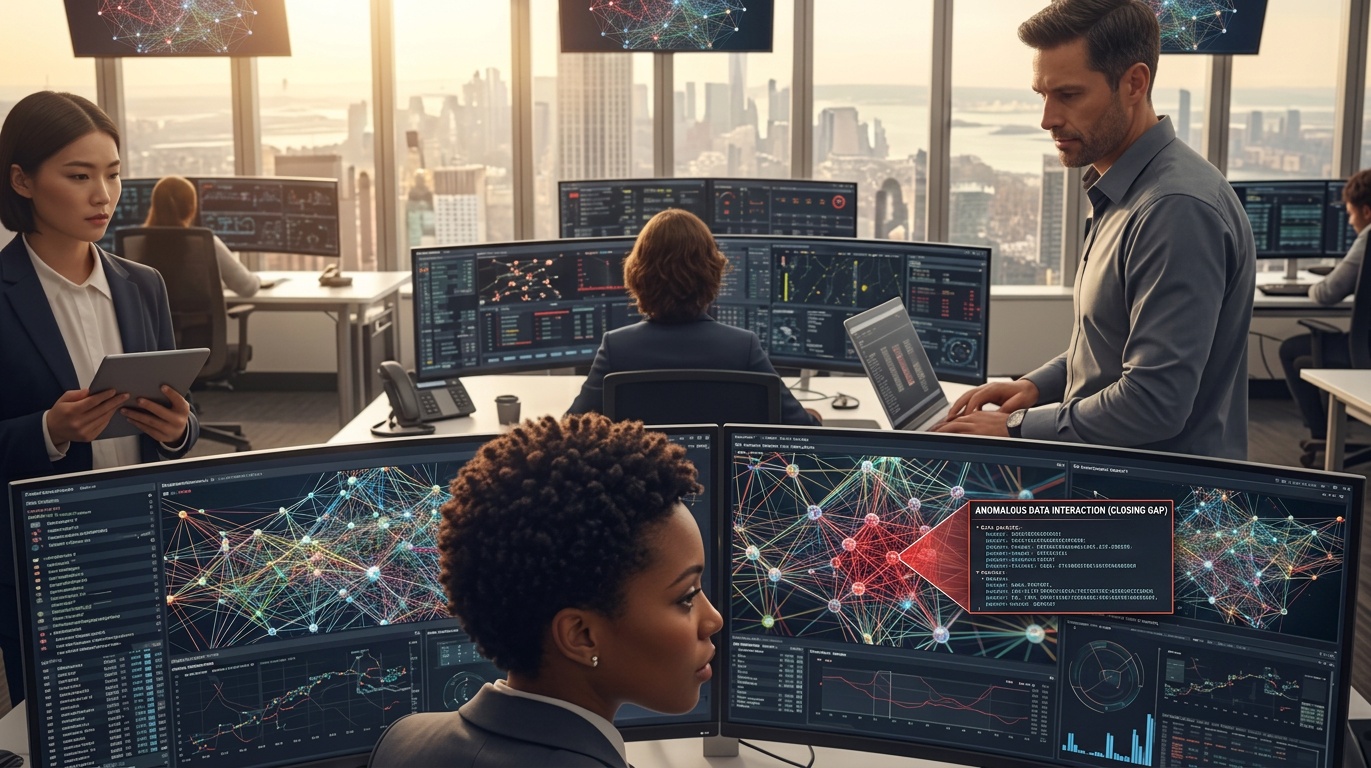
Autonomous security agents are becoming increasingly popular in the cybersecurity industry, with many organizations adopting them to improve their security posture. However, these agents require complete data to function effectively, and current systems often have blind spots that can leave them vulnerable to attacks.
According to the 2026 Axonius Actionability Report, conducted with the Ponemon Institute, 12.7% of devices in a 298,000-device median inventory are missing their expected security agent. This gap in coverage can have significant consequences, as autonomous agents will query the same dashboards, trust the same coverage percentages, and act on the same blind spots that human analysts have learned to work around.
The use of autonomous security agents is expected to continue growing in the coming years, with many organizations looking to automate their security operations to improve efficiency and reduce costs. However, the effectiveness of these agents depends on the quality and completeness of the data they receive. Incomplete or inaccurate data can lead to false positives, false negatives, and other errors that can compromise the security of the organization.
The Importance of Complete Data for Autonomous Security Agents
Complete data is essential for autonomous security agents to function effectively. Without it, these agents may not be able to detect and respond to security threats in a timely and effective manner. The following are some reasons why complete data is crucial for autonomous security agents:
- Improved threat detection: Complete data allows autonomous security agents to detect threats more accurately and respond to them in a timely manner.
- Enhanced incident response: With complete data, autonomous security agents can respond to security incidents more effectively, reducing the risk of damage and downtime.
- Better decision-making: Complete data enables autonomous security agents to make more informed decisions, reducing the risk of false positives and false negatives.
In addition to improving the effectiveness of autonomous security agents, complete data can also help organizations to improve their overall security posture. By providing a comprehensive view of the organization's security landscape, complete data can help organizations to identify vulnerabilities and weaknesses, and to prioritize their security efforts accordingly.
Complete data can also help organizations to comply with regulatory requirements and industry standards. Many regulations, such as the General Data Protection Regulation (GDPR) and the Payment Card Industry Data Security Standard (PCI DSS), require organizations to have robust security controls in place to protect sensitive data. Complete data can help organizations to demonstrate compliance with these regulations and to avoid costly fines and penalties.
Challenges in Achieving Complete Data for Autonomous Security Agents
Achieving complete data for autonomous security agents can be challenging, as it requires a comprehensive understanding of the organization's security posture and the ability to collect and analyze data from various sources. Some of the challenges that organizations may face in achieving complete data include:
- Data silos: Organizations may have data silos that make it difficult to collect and analyze data from various sources.
- Legacy systems: Legacy systems may not be able to provide the necessary data to support autonomous security agents.
- Scalability: Organizations may need to scale their data collection and analysis capabilities to support the growing demands of autonomous security agents.
Another challenge that organizations may face is the complexity of their security landscape. Many organizations have complex security environments, with multiple systems, applications, and devices that need to be monitored and protected. This complexity can make it difficult to collect and analyze data, and to provide complete data to autonomous security agents.
Additionally, organizations may face challenges in integrating data from various sources, including cloud-based applications, on-premises systems, and IoT devices. This integration can be difficult due to differences in data formats, protocols, and architectures, and can require significant resources and expertise.
Best Practices for Ensuring Complete Data for Autonomous Security Agents
To ensure that autonomous security agents have the complete data they need to function effectively, organizations should follow best practices such as:
- Implementing a comprehensive data collection and analysis strategy.
- Integrating data from various sources, including legacy systems and cloud-based applications.
- Using machine learning and artificial intelligence to analyze data and identify patterns and anomalies.
By following these best practices, organizations can ensure that their autonomous security agents have the complete data they need to function effectively and improve their overall security posture. Additionally, organizations should regularly review and update their data collection and analysis capabilities to ensure that they are keeping pace with the evolving threat landscape.
Organizations should also consider implementing a security information and event management (SIEM) system to collect and analyze data from various sources. A SIEM system can provide a comprehensive view of the organization's security landscape, and can help to identify vulnerabilities and weaknesses.
In conclusion, complete data is essential for autonomous security agents to function effectively. Organizations should follow best practices to ensure that their autonomous security agents have the complete data they need to improve their overall security posture.
Real-World Examples of Autonomous Security Agents
There are many real-world examples of autonomous security agents being used to improve the security posture of organizations. For example, some organizations are using autonomous security agents to monitor and respond to security incidents in real-time. These agents can analyze data from various sources, including network logs, system logs, and threat intelligence feeds, to identify potential security threats and respond to them quickly.
Other organizations are using autonomous security agents to improve their incident response capabilities. These agents can analyze data from various sources to identify the root cause of a security incident, and can provide recommendations for remediation and mitigation.
Autonomous security agents are also being used to improve the security of IoT devices. These agents can monitor and analyze data from IoT devices to identify potential security threats, and can respond to them quickly to prevent attacks.
Future of Autonomous Security Agents
The use of autonomous security agents is expected to continue growing in the coming years, as organizations look to improve their security posture and reduce the risk of cyber attacks. As the threat landscape continues to evolve, autonomous security agents will play an increasingly important role in helping organizations to stay ahead of threats.
In the future, we can expect to see more advanced autonomous security agents that can analyze data from various sources, including social media, news feeds, and other external sources. These agents will be able to provide more comprehensive and accurate threat intelligence, and will be able to respond to security incidents more quickly and effectively.
Additionally, we can expect to see more integration of autonomous security agents with other security technologies, such as SIEM systems, threat intelligence platforms, and security orchestration, automation, and response (SOAR) systems. This integration will enable organizations to create more comprehensive and automated security systems that can detect and respond to security threats in real-time.
This article was written by the Pitchbar tech news editor for the startup community, with information sourced from venturebeat.com.