Introduction to AI Security Risks
The recent disclosures of security vulnerabilities in Microsoft 365 Copilot Enterprise Search and LiteLLM have highlighted the importance of trust boundaries in enterprise AI tools. Two research teams, Varonis and Obsidian Security, have demonstrated how these tools can be exploited to gain unauthorized access to sensitive data.
The pattern underlying these disclosures is the lack of trust boundaries in enterprise AI tools, which accept external input without proper validation. This can lead to serious security risks, including data exfiltration and remote code execution.
Furthermore, the increasing use of AI tools in enterprise environments has created new attack surfaces that can be exploited by malicious actors. As AI tools become more pervasive, it is essential to ensure that they are designed and implemented with security in mind.
In addition, the lack of transparency and explainability in AI decision-making processes can make it challenging to identify and mitigate security risks. Therefore, it is crucial to develop and implement AI tools that are transparent, explainable, and secure.
Copilot's SearchLeak Vulnerability
Copilot's SearchLeak vulnerability, disclosed by Varonis, allows an attacker to craft a malicious URL that can search a victim's mailbox and exfiltrate sensitive data. This vulnerability is particularly concerning, as it requires no plugins, no second click, and no visible indicator.
The SearchLeak vulnerability is a result of three weaknesses chained together: a rendering race condition, a URL parameter that feeds attacker instructions straight to Copilot's LLM, and a Bing SSRF that allows data to leave the system.
The SearchLeak vulnerability highlights the importance of proper input validation and trust boundaries in enterprise AI tools. It also underscores the need for continuous monitoring and testing of AI tools to identify and mitigate potential security risks.
In order to mitigate the SearchLeak vulnerability, it is essential to implement robust input validation and trust boundaries in Copilot and other enterprise AI tools. This can include implementing strict URL parameter validation, using secure protocols for data transmission, and regularly updating and patching AI tools.
LiteLLM's Three-CVE Chain
Obsidian Security published a three-CVE chain against LiteLLM, which carried a default low-privilege user all the way to admin and remote code execution. This vulnerability highlights the importance of proper input validation and trust boundaries in enterprise AI tools.
The three-CVE chain against LiteLLM demonstrates how a lack of trust boundaries can lead to serious security risks, including admin access and remote code execution.
The LiteLLM vulnerability also underscores the need for secure coding practices and regular security audits in the development of enterprise AI tools. By implementing secure coding practices and conducting regular security audits, developers can identify and mitigate potential security risks in AI tools.
Moreover, the LiteLLM vulnerability highlights the importance of implementing least privilege access controls in enterprise AI tools. By limiting user privileges to the minimum required for their roles, organizations can reduce the risk of security breaches and data exfiltration.
5-Check Audit to Protect Your Stack
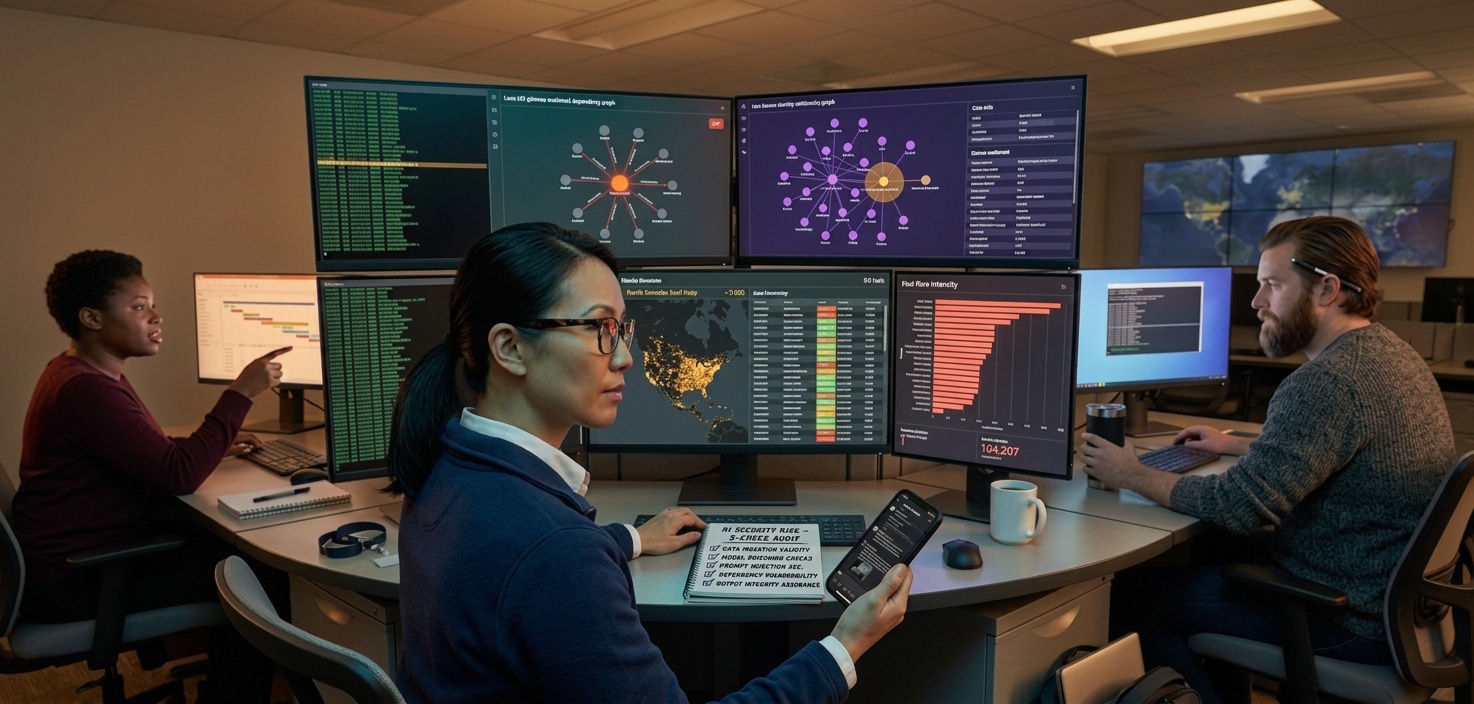
To protect your stack from AI security risks, it's essential to run a 5-check audit. This audit should include:
- Reviewing your AI tool's input validation and trust boundaries
- Checking for any known vulnerabilities in your AI tools
- Verifying that your AI tools are properly configured and updated
- Monitoring your AI tools for any suspicious activity
- Conducting regular security audits and penetration testing
By following these steps, you can help protect your stack from AI security risks and ensure the security and integrity of your data.
In addition to the 5-check audit, it is also essential to implement a comprehensive security strategy that includes employee education and awareness, incident response planning, and continuous monitoring and testing of AI tools.
Organizations should also consider implementing a bug bounty program to encourage responsible disclosure of security vulnerabilities in their AI tools. This can help identify and mitigate potential security risks before they can be exploited by malicious actors.
Conclusion and Recommendations
In conclusion, the recent disclosures of security vulnerabilities in Microsoft 365 Copilot Enterprise Search and LiteLLM highlight the importance of trust boundaries and input validation in enterprise AI tools.
To protect your stack from AI security risks, it is essential to implement a comprehensive security strategy that includes regular security audits, penetration testing, and continuous monitoring of AI tools.
Organizations should also consider implementing secure coding practices, least privilege access controls, and bug bounty programs to encourage responsible disclosure of security vulnerabilities.
This article was written by the Pitchbar tech news editor for the startup community, with the goal of providing actionable advice and insights to founders and builders. Source: venturebeat.com, URL: https://venturebeat.com/security/copilot-searched-your-mailbox-litellm-handed-out-admin